Enterprise Cryptographic Risk Management
SafeLogic Cryptographic Posture Management (CPM)
Discover, understand, remediate, and continuously
govern cryptographic risk with an agentless-first,
modular platform.
Agentless-
First
Multi-Source Discovery
Application-aware prioritization
Integrated remediation
Continuous governance
Find Cryptographic Risk.
Understand Where it Matters.
Fix it—and Keep it from Coming Back.
SafeLogic Cryptographic Posture Management (CPM) helps enterprises discover cryptography across applications, infrastructure, networks, cloud environments, repositories, and development pipelines—starting with agentless scans, APIs, integrations, and data they already collect. Optional targeted telemetry adds deeper visibility where it provides meaningful value.
SafeLogic CPM brings cryptographic findings together with application, runtime, and business context so organizations can prioritize risk, accelerate remediation, enforce cryptographic policy, and prepare for the post-quantum transition.
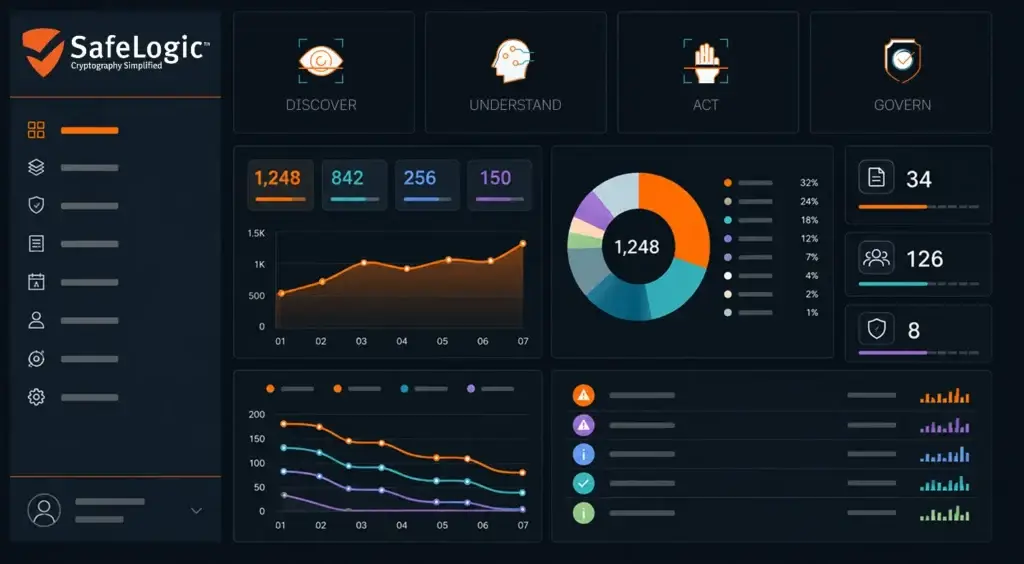
Discover
UNDERSTAND
ACT
Govern
Cryptographic Risk Is Hiding in Plain Sight
Cryptography is distributed across application code, open-source libraries, frameworks, operating systems, certificates, network connections, cloud infrastructure, and third-party dependencies.
Much of it may not have been selected directly by your development team. It may be inherited from a framework, embedded in a dependency, configured by a platform, or introduced through infrastructure that has changed over time.
Traditional scanners can identify algorithms and libraries that appear to be present. But static discovery alone cannot always answer the questions security and engineering teams need to act:
- Is the cryptography actually being used?
- How often is it running?
- Which application or business service depends on it?
- Did it originate in application code, a framework, a platform, or a provider?
- Is the finding an immediate operational risk?
- Will remediation require a rewrite, a configuration change, or replacement software?
Without this context, every finding can appear equally urgent—and migration programs stall.
Effective enterprise cryptography management requires more than a point-in-time scan. Security teams need an operational view of what cryptography exists, where it is used, which systems depend on it, and what should be remediated first.
Broad, Modular Discovery Across Your
Cryptographic Estate
SafeLogic CPM builds a broad, usable view of cryptography across code, applications, infrastructure, networks, cloud environments, dependencies, repositories, and development pipelines. Its agentless-first, modular approach can generate findings, enrich an existing inventory, or ingest discovery data from other tools, with optional targeted collectors and runtime telemetry providing deeper visibility where needed.
Agentless Discovery
Start with remote network and TLS scanning, cloud and infrastructure APIs, repository and dependency analysis, CI/CD integrations, and telemetry your organization already collects.
Integrated Discovery Data
Bring third-party findings, CMDB and SIEM context, certificate inventories, CBOMs, asset information, and other enterprise data into a unified cryptographic view.
Optional Targeted Visibility
Add host collectors, runtime instrumentation, or SafeLogic library telemetry for selected applications and environments where deeper operational evidence improves prioritization.
The Full Cryptographic Lifecycle
Discover
UNDERSTAND
ACT
Govern
See how SafeLogic CPM brings together agentless-first discovery, multi-source cryptographic data, application and business context, prioritized remediation, and continuous policy enforcement in one connected lifecycle.
We Don’t Just Discover Cryptography.
We Watch It Run.
A static scanner can identify an algorithm, library, or dependency that is present. When deeper visibility is needed, SafeLogic CPM can add optional runtime evidence to show whether that cryptography is actively used, how frequently it executes, what application path invokes it, and where remediation should occur.
SafeLogic CPM adds runtime evidence that can reveal:
- Which cryptographic operations are actively executing
- How often and where they are being used
- The application, framework, platform, and provider behind each call
- Cryptography observed at runtime but missing from declared inventories
- Whether remediation may require code changes, configuration changes, or replacement software
That context can be the difference between planning a major
rewrite and making a targeted configuration change.
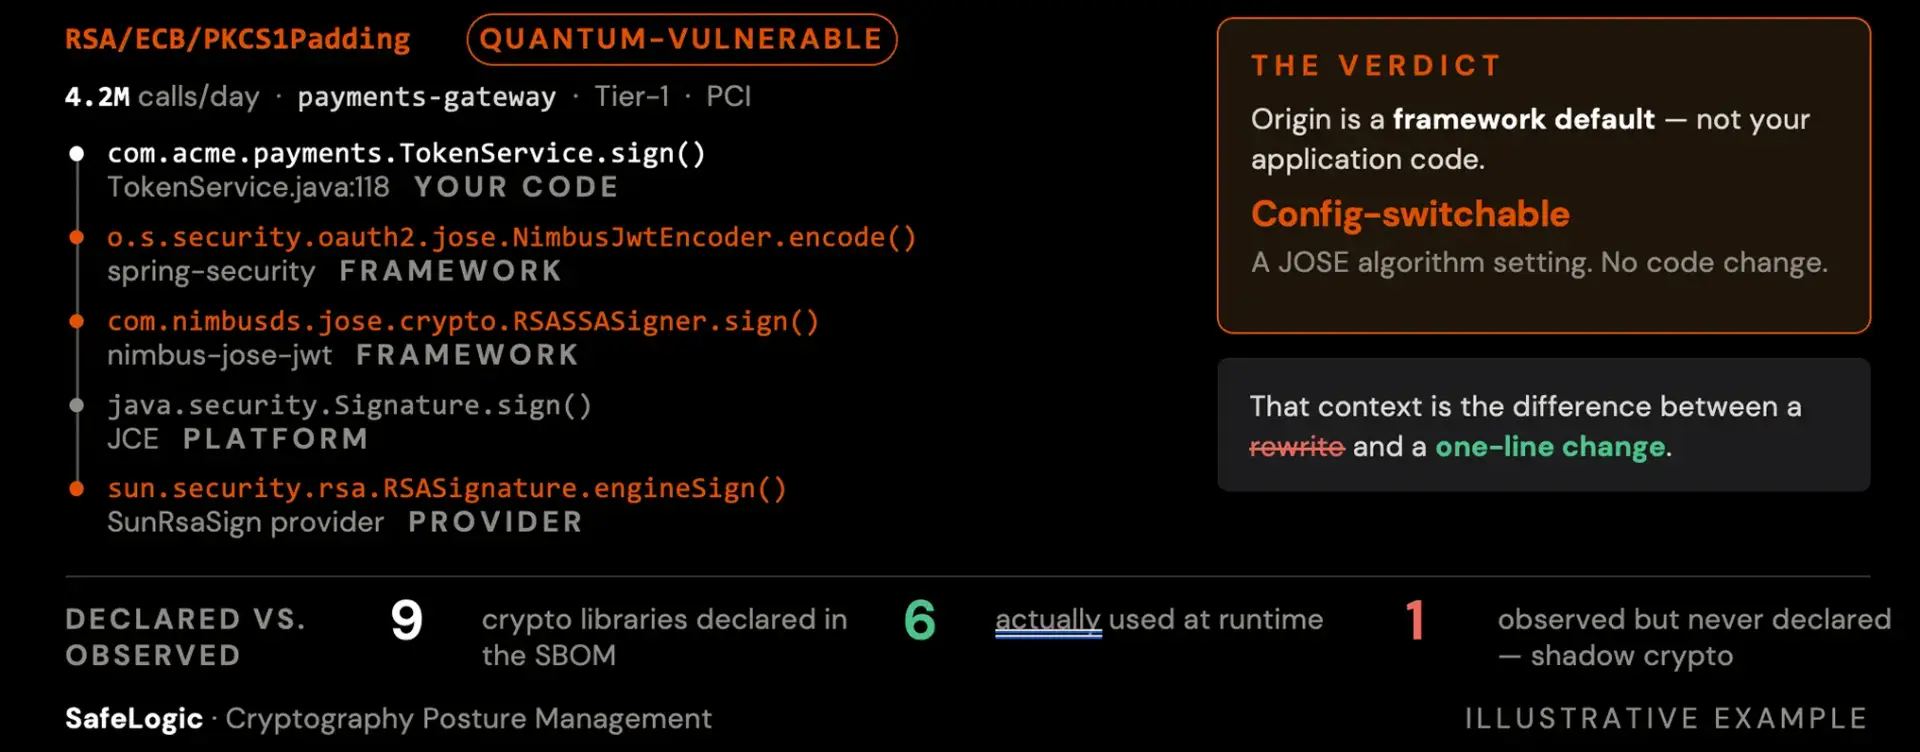
Illustrative example of how SafeLogic CPM traces cryptographic activity at runtime,
identifies its origin across the application stack, and helps determine the appropriate
remediation path.
Build and Maintain a Cryptographic
Asset Inventory
Turn disconnected findings into a continuously updated operational cryptographic inventory.
SafeLogic CPM brings findings from code, hosts, networks, supported runtime telemetry, external tools, and enterprise systems into one unified inventory. This approach to cryptographic inventory management helps teams see what cryptography exists, where it runs, who owns it, which applications depend on it, whether it is actively used, which policies apply, and how it may be remediated.
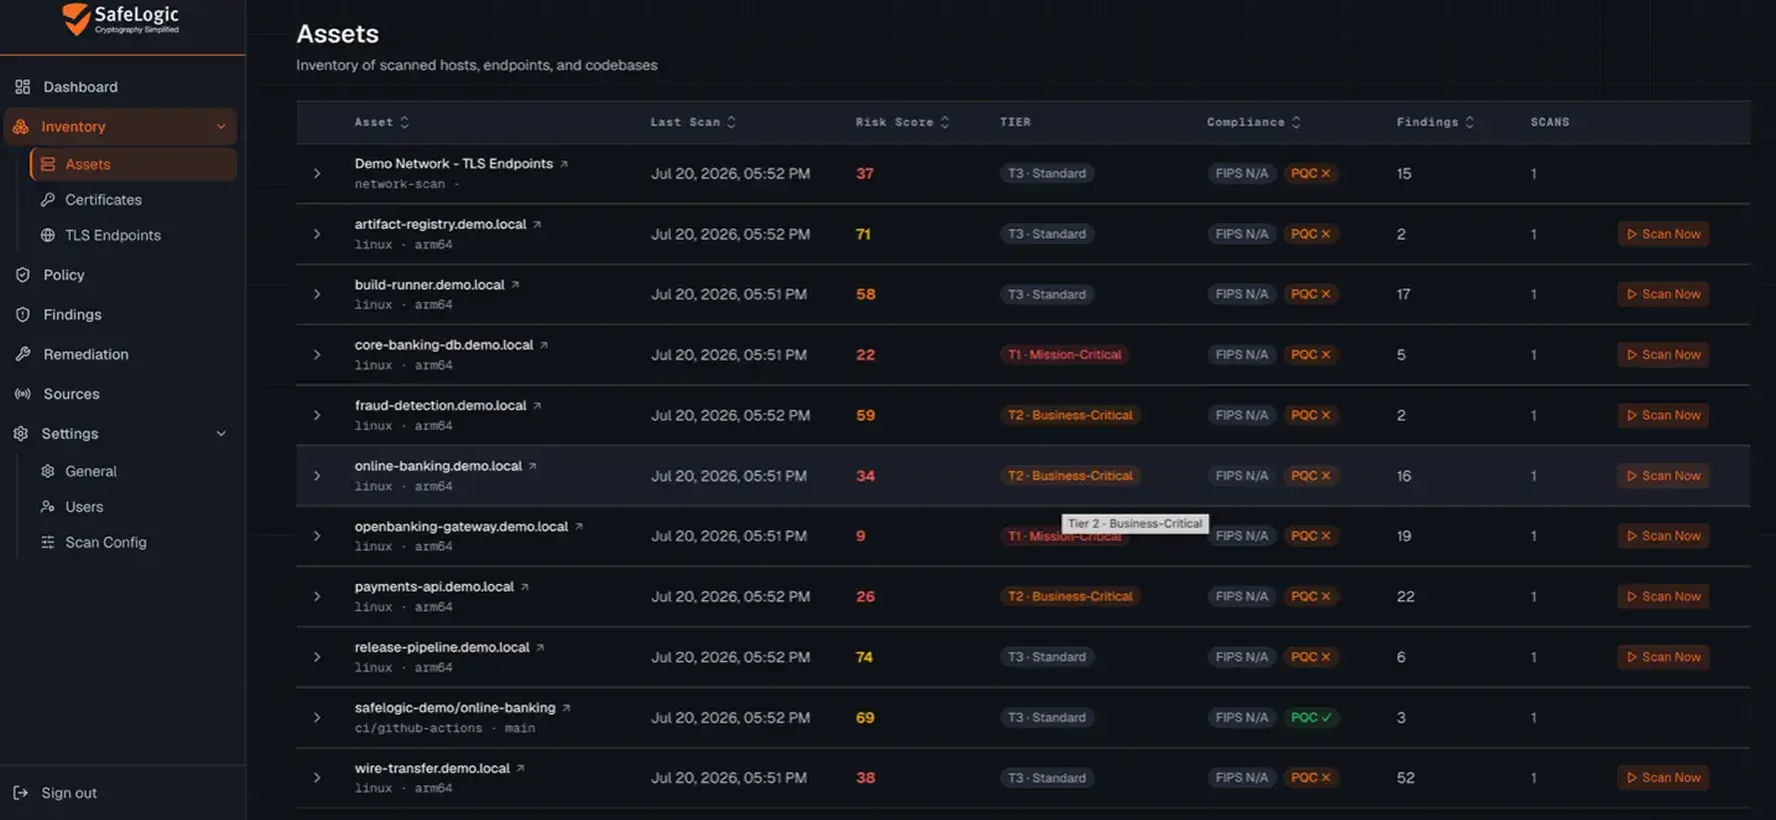
SafeLogic CPM correlates cryptographic findings across applications and environments to provide the visibility needed to prioritize risk and plan post-quantum migration.
Build an Operational CBOM That Evolves
with Your Environment
SafeLogic CPM generates and maintains a CycloneDX Cryptographic Bill of Materials that can be used across security, development, compliance, architecture, and risk-management workflows.
An operational CBOM can support:
- PQC Migration Planning
- Cryptographic Risk Management
- Compliance and Audit Evidence
- Software Supply Chain Visibility
- Ownership and Remediation Tracking
- Continuous Verification as Applications Change
Unlike a static CBOM generated during a point-in-time assessment, an operational CBOM reflects changes in deployed software, certificates, dependencies, configurations, and observed cryptographic activity.
Turn Cryptographic Findings into
a Ranked Action Queue
Security teams need to know which cryptographic risks matter most.
Discovery can produce thousands of findings. SafeLogic CPM correlates cryptographic evidence with business and operational context so teams can focus on the risks that matter most.
The analysis engine can evaluate factors including:
- Quantum vulnerability
- Application criticality
- External exposure
- Data sensitivity
- Runtime activity
- Compliance and policy status
Integrations with platforms such as ServiceNow CMDB and Splunk SIEM add ownership, application tier, data classification, and observed exposure to the analysis.
The result is a prioritized action queue that shows what is actively at risk, what is truly exposed, which systems matter most, and whether remediation requires a configuration change or a larger engineering effort.
By combining cryptographic evidence with business context, SafeLogic CPM supports risk-based enterprise cryptographic risk management rather than treating every finding as equally urgent.
Signal beats assumption. Live operational evidence can override stale asset records and reprioritize risk based on what is happening now.
Remediate Risk—and Verify the
New Path Is Running
Cryptographic discovery alone stops at the finding. SafeLogic CPM connects findings with a path to remediation through SafeLogic’s production-ready classical, hybrid, and post-quantum cryptographic software.
Depending on the finding, remediation may involve:
- Adjusting an application or framework configuration
- Replacing an outdated cryptographic library
- Enforcing an approved algorithm policy
- Deploying FIPS 140-3 validated cryptography with CryptoComply
- Deploying NIST-standardized PQC with SafePQ
- Updating certificates, protocols, or TLS configurations
- Verifying through subsequent scans or supported runtime telemetry that the intended cryptographic path is active
One Cryptographic Policy.
Three Layers of Enforcement.
SafeLogic CPM helps operationalize cryptographic policy
throughout development, deployment, and production.
Detect
Evaluate code, systems, network configurations, and supported runtime activity against policies such as CNSA 2.0, FIPS 140-3 requirements, or organization-specific standards.
Correct
Turn prioritized findings into controlled remediation actions, including configuration changes and deployment of trusted classical, hybrid, or post-quantum cryptographic software.
Prevent
Integrate policy into CI/CD workflows and deploy policy-enforcing SafeLogic cryptographic software to block or flag noncompliant algorithm selection and reduce the risk of reintroduction.
Enterprise-Ready Integrations
SafeLogic CPM complements the certificate, endpoint, cloud, asset-management, and security platforms enterprises already operate. It brings their findings into a unified cryptographic-risk model while adding deeper application context, prioritization, remediation, and governance.
- ServiceNow CMDB
- Splunk SIEM
- CI/CD Pipeline
- CycloneDX CBOM Ecosystem
- APIs & Data Export
- Enterprise Development Workflows
Enterprise Software &
Cryptography Expertise
SafeLogic CPM is backed by cryptographic engineers, solution architects, and enterprise support teams experienced in FIPS 140, post-quantum cryptography, cryptographic integration, and production software deployment.
SafeLogic helps organizations deploy CPM, integrate it with existing workflows, interpret findings, and connect identified risks with a practical cryptographic modernization path.
Planning a broader cryptographic modernization program?
From Discovery to Continuous Cryptographic Governance
DISCOVER BROADLY
Build a usable cryptographic inventory across applications, infrastructure, networks, cloud environments, repositories, and development pipelines using modular, agentless-first discovery.
Understand What Matters
Connect cryptographic findings to applications, dependencies, operational use, owners, business assets, exposure, and criticality to identify where risk matters most.
Act on Risk
Prioritize actionable issues and provide practical remediation paths for custom applications, dependencies, configurations, protocols, certificates, and cryptographic libraries.
Govern Continuously
Define and enforce cryptographic policy, monitor for drift, generate evidence, guide developers, and help prevent vulnerable or noncompliant cryptography from being reintroduced.
Ready to Find, Fix, and Govern
Cryptographic Risk?
Call us at 844.436.2797 or complete the form below to talk to a cryptography expert.
Latest Insights
Stay informed on cryptographic risk management, PQC readiness, cryptographic inventory, and evolving security requirements.