Get FIPS 140-3 Validated in
Only 90 Days with SafeLogic
Cut the red tape, quickly secure your FIPS 140-3 certification, and stay compliant for years.
Everything You Need to Know About FIPS 140-3 Validation
From Basics to SafeLogic’s Accelerated Strategy
Navigating FIPS 140-3 validation can be complex, but it’s essential for ensuring that your cryptographic modules meet the highest federal security standards.
In this comprehensive guide, SafeLogic’s cryptography experts walk you through everything you need to know—from the history and benefits of FIPS 140-3 to the challenges and transition from FIPS 140-2.
Whether you’re new to FIPS or need to update from FIPS 140-2, this guide is your essential resource for success.
Inside You’ll Learn:
- About FIPS 140-3: History, Benefits and Challenges
- Transitioning from FIPS 140-2 to FIPS 140-3
- What is Required to Get FIPS 140-3 Validated?
- What Does the Future Entail for FIPS 140-3?
- SafeLogic’s FIPS 140-3 Strategy
Fast-track your path to FIPS 140-3 validation and certification.
Complete the form to download the eBook now!
Why It's Worth Getting Your Product
FIPS 140-3 Certified & Validated
Public Sector Access
Unlocks eligibility to sell to the government and regulated industries that require FIPS 140-3 compliance
Enhanced Security
Ensures your products meet stringent encryption standards, boosting trust and protecting sensitive data
Competitive Advantage
Differentiates your product with a certification in your company's name that signals top-tier security to customers and partners
Traditional FIPS 140 Validation is
Time-Consuming, Frustrating and Costly
Traditional FIPS 140-3 validation has three main phases: Documentation, Testing, and Validation. It requires extensive collaboration with a FIPS consultant, your NIST-authorized certification lab, and NIST itself.
This process can take two+ years, not counting the time required to develop the cryptography software. More recently, as the industry has been transitioning from FIPS 140-2 to FIPS 140-3, this process has been taking much longer.
Even worse, FIPS Validation is not a one-time project, expense, and headache. FIPS validated software often needs to be revalidated due to CVEs and changing requirements. Otherwise, your FIPS certificate will go ‘historical’, and you will no longer be able to use it to support new federal acquisitions.
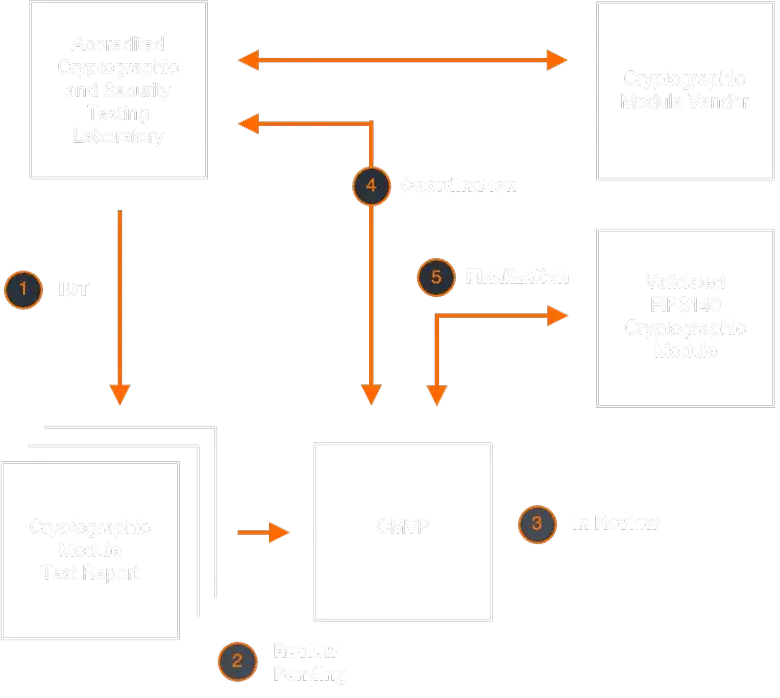
Going for validation on your own is not for the faint of heart. But this is not the only option. SafeLogic’s unique FIPS 140-Validated Software can get you a FIPS 140-3 certificate in your own company’s name in just two months, versus the two years it normally takes.
Important to Note: FIPS 140-3 Compliant
is not the same as FIPS 140-3 Validated
Compliant, validated, and certified are NOT synonyms when it comes to FIPS 140-3. Thinking they are can lead to costly mistakes.
FIPS 140 Validated means your company's cryptographic module has passed a formal testing process with a NIST-approved lab and received a FIPS validation certificate in your company’s name. This certificate is listed publicly.
FIPS 140-3 Compliant uses a FIPS 140 validated cryptographic module from an open-source, OS or cloud services provider. While this might seem like a good idea, this FIPS compliance strategy is extremely risky for two reasons:
- FIPS 140-3 compliant today may not be FIPS compliant tomorrow if someone else’s module goes out of compliance (e.g., goes Historical). This often happens when a vendor declares an older product ‘end-of-life’. When that happens, it’s your public sector sales that are at risk.
- Government procurement agents may block the acquisition of products that do not have FIPS certification in their own name in the CMVP database. They will want to see that the CMVP certificate has an organization’s specific details.
SafeLogic’s CryptoComply customers don’t have these challenges. Our FIPS 140-3 validated software offerings can get FIPS 140-3 certificates and listings in the CMVP database in your company’s name. And it takes just 90 days, not two years! Then we maintain the software and your FIPS 140 certifications, ensuring you remain in “Active” status until your sunset dates.
Why Choose SafeLogic for
FIPS 140-3 Validation?
Get FIPS 140-3 Validated Faster, Launch Sooner, Maintain Certification Over Time
SafeLogic speeds up FIPS 140-3 validation, getting you certified in a fraction of the usual time. Get your product to market quicker, saving valuable time and driving revenue sooner.
With SafeLogic, you don’t just comply—you get fully validated, meaning the certification is in your name or your company’s name. This ensures you maintain control and credibility.
Leverage SafeLogic’s FIPS 140-3 experts to streamline your process, freeing up your team to focus on higher-value projects while enjoying predictable, fixed costs over time.
Ensure you remain in good standing with changing NIST FIPS 140 requirements. Our experts help navigate evolving standards seamlessly so you stay compliant without disruption or delays.
Three Unique FIPS 140-3 Offerings
Keep You Secure and Validated... Fast!
Getting your cryptographic software certified by NIST for FIPS 140-3 can take two or more years. SafeLogic slashes that timeline to just 90 days and ensures your certification stays active with the following three key capabilities.
Click on the boxes below to learn more about each of our FIPS 140-3 service offerings.
CryptoComply
CryptoComply is SafeLogic’s flagship software, a family of FIPS 140 validated cryptographic software modules. They deliver “Drop-in Compliance” as direct replacements for popular open-source crypto providers.
RAPIDCERT
SafeLogic revolutionized the FIPS industry twelve years ago with RapidCert, the industry’s first expedited rebranding program. Get FIPS certification of your CryptoComply solution, in your name, in only two months with RapidCert.
MAINTAINCERT
Now SafeLogic is revolutionizing FIPS again with MaintainCert. FIPS certificates go ‘historical’, meaning they are no longer valid, all the time. Not with MaintainCert, SafeLogic’s new white-glove support service.
SafeLogic is Trusted By:
FAQs
What is fips 140 certification?
FIPS 140 certification is a U.S. government standard that specifies security requirements for cryptographic modules used within any government system with encryption to protect sensitive information.
Why is FIPS 140 certification important?
It ensures that cryptographic products meet federal security standards, making them reliable for protecting sensitive data, especially in government and regulated industries. If you don’t have FIPS 140 certification, procurement agents can block the purchase of your product.
What are the levels of FIPS 140 certification?
The FIPS 140-3 standard provides four increasing, qualitative levels of security: Level 1, Level 2, Level 3, and Level 4. These levels are intended to cover the wide range of potential applications and environments in which cryptographic modules may be employed. Each subsequent level builds upon the requirements of the previous level. These levels are clearly indicated on each validation certificate. The strength and functionality of the cryptography is the same for each level.
Do I need FIPS 140 validation for FedRAMP, StateRAMP, CMMC, Common Criteria, and DoDINAPL?
In short, yes. These government programs have all been built using NIST publications as building blocks, so they all reference NIST’s existing advisories and guidance on the proper usage of cryptography, known as FIPS 140.
For more technical insight on specific programs and dependencies, check out our repository of whitepapers.
How long does the FIPS 140 certification process take?
Traditionally, the certification process can take two or more years, depending on the complexity of the cryptographic module and the validation back log. However, with solutions like SafeLogic, it can be expedited to around three to four months.
Who conducts the FIPS 140 certification?
The certification is conducted by the National Institute of Standards and Technology (NIST) and its Canadian equivalent through the Cryptographic Module Validation Program (CMVP). Accredited laboratories evaluate cryptographic modules to ensure compliance with FIPS 140 standards.
What is the difference between FIPS 140-2 and FIPS 140-3?
FIPS 140-3 is the updated version of the standard, which includes new security requirements and addresses advances in technology and cryptography, while FIPS 140-2 is the older version.
What types of products need FIPS 140 certification?
Any product that uses cryptography to secure sensitive information sold to the government, including software applications, hardware devices, and firmware, may require FIPS 140 certification.
How often do I need to renew my FIPS 140 certification?
FIPS 140 certification expires every five years. Maintaining compliance with evolving standards and conducting regular reviews of your cryptographic module is essential.
Can I use a non-FIPS certified product for government projects?
No. Government agencies require FIPS 140 certified products to ensure compliance with federal regulations when handling sensitive data.
How can SafeLogic help with FIPS 140 certification?
SafeLogic streamlines the certification process, reducing the time to achieve FIPS 140 certification from two years to two months, and offers ongoing support to maintain certification over time.
CryptoComply Supports a Broad Range of
Platform Types, Operating Systems, Languages,
and Open Source Modules Including ...
Drop-In Compliance
Mobile Device
Android
iOS
iPadOS